NFTIME Inc. (the “Company”), as an information and communications service provider, complies with the personal information protection provisions of applicable laws, including the Personal Information Protection Act, and has established this Privacy Policy under those laws to protect users’ rights. This Privacy Policy applies to the Certi service provided by the Company (including the “User Service,” the “Admin Service,” and all related services). This English version is a translation provided for convenience; if it conflicts with the Korean original, the Korean version prevails.
Article 1 (General)
“Personal information” means information about a living individual that can identify that individual by name, contact details, or other items included in it (including information that cannot identify a specific individual on its own but can easily be combined with other information to do so).
The Company values users’ personal information and complies with applicable laws, including the Personal Information Protection Act and the Act on Promotion of Information and Communications Network Utilization and Information Protection.
Through this Privacy Policy, the Company informs users of the purposes and ways in which the personal information they provide is used, and of the measures taken to protect it.
The Company publishes this Privacy Policy on the Service’s initial screen so that users can easily view it at any time.
The Company’s Privacy Policy may change from time to time due to changes in government laws and guidelines or the Company’s internal policies, and the Company has established the procedures necessary to continually improve it. When the Privacy Policy is revised, the Company posts the changes through service notices, and users can check them at any time.
Article 2 (Purposes of Processing Personal Information)
The Company processes personal information for the following purposes. Personal information is not used for any purpose other than those below, and if the purpose of use changes, the Company will take necessary measures, such as obtaining separate consent under Article 18 of the Personal Information Protection Act.
Member identification and management: confirming the intention to sign up of users of the “User Service” (“User Members”) and the “Admin Service” (“Admin Members”), identifying and authenticating members, maintaining and managing membership, preventing misuse of the service, sending notices, and keeping records for dispute resolution
Providing the digital badge service:
(Admin Members) creating programs, designing and creating digital badges, managing recipients, and more
(User Members) receiving, storing, viewing, integrating into portfolios, and sharing externally (LinkedIn integration, etc.) digital badges
Issuing and delivering digital badges: sending digital badges to recipients via KakaoTalk or email at the request of Admin Members
Providing paid services: providing paid plan (subscription) services for Admin Members, processing and settling payments, and managing ‘badge issuance credits’
Storing, viewing, sharing, and verifying digital badges: receiving, storing, viewing, sharing externally, and integrating digital badges into portfolios; generating and downloading PDF certificates; confirming issuance and verifying authenticity through verification pages, share links, and QR codes; providing proof functions for previously issued digital badges; and preventing fraudulent issuance and handling disputes
Developing new services and use for marketing and advertising:
Analyzing digital badge information held, service usage records, and similar data with AI (artificial intelligence) technology to recommend personalized education programs and job postings
Developing new services and providing customized services, providing services and displaying advertising based on statistical characteristics, confirming the effectiveness of services, providing event information and opportunities to participate, measuring access frequency, and compiling statistics on members’ use of the service
Handling complaints: confirming the identity of complainants, checking complaints, contacting and notifying for fact-finding, and notifying results
Article 3 (Personal Information Processed and Collection Methods)
The Company discloses the personal information items it collects ‘directly’ to provide the Service, by member type, as follows.
Personal information collected
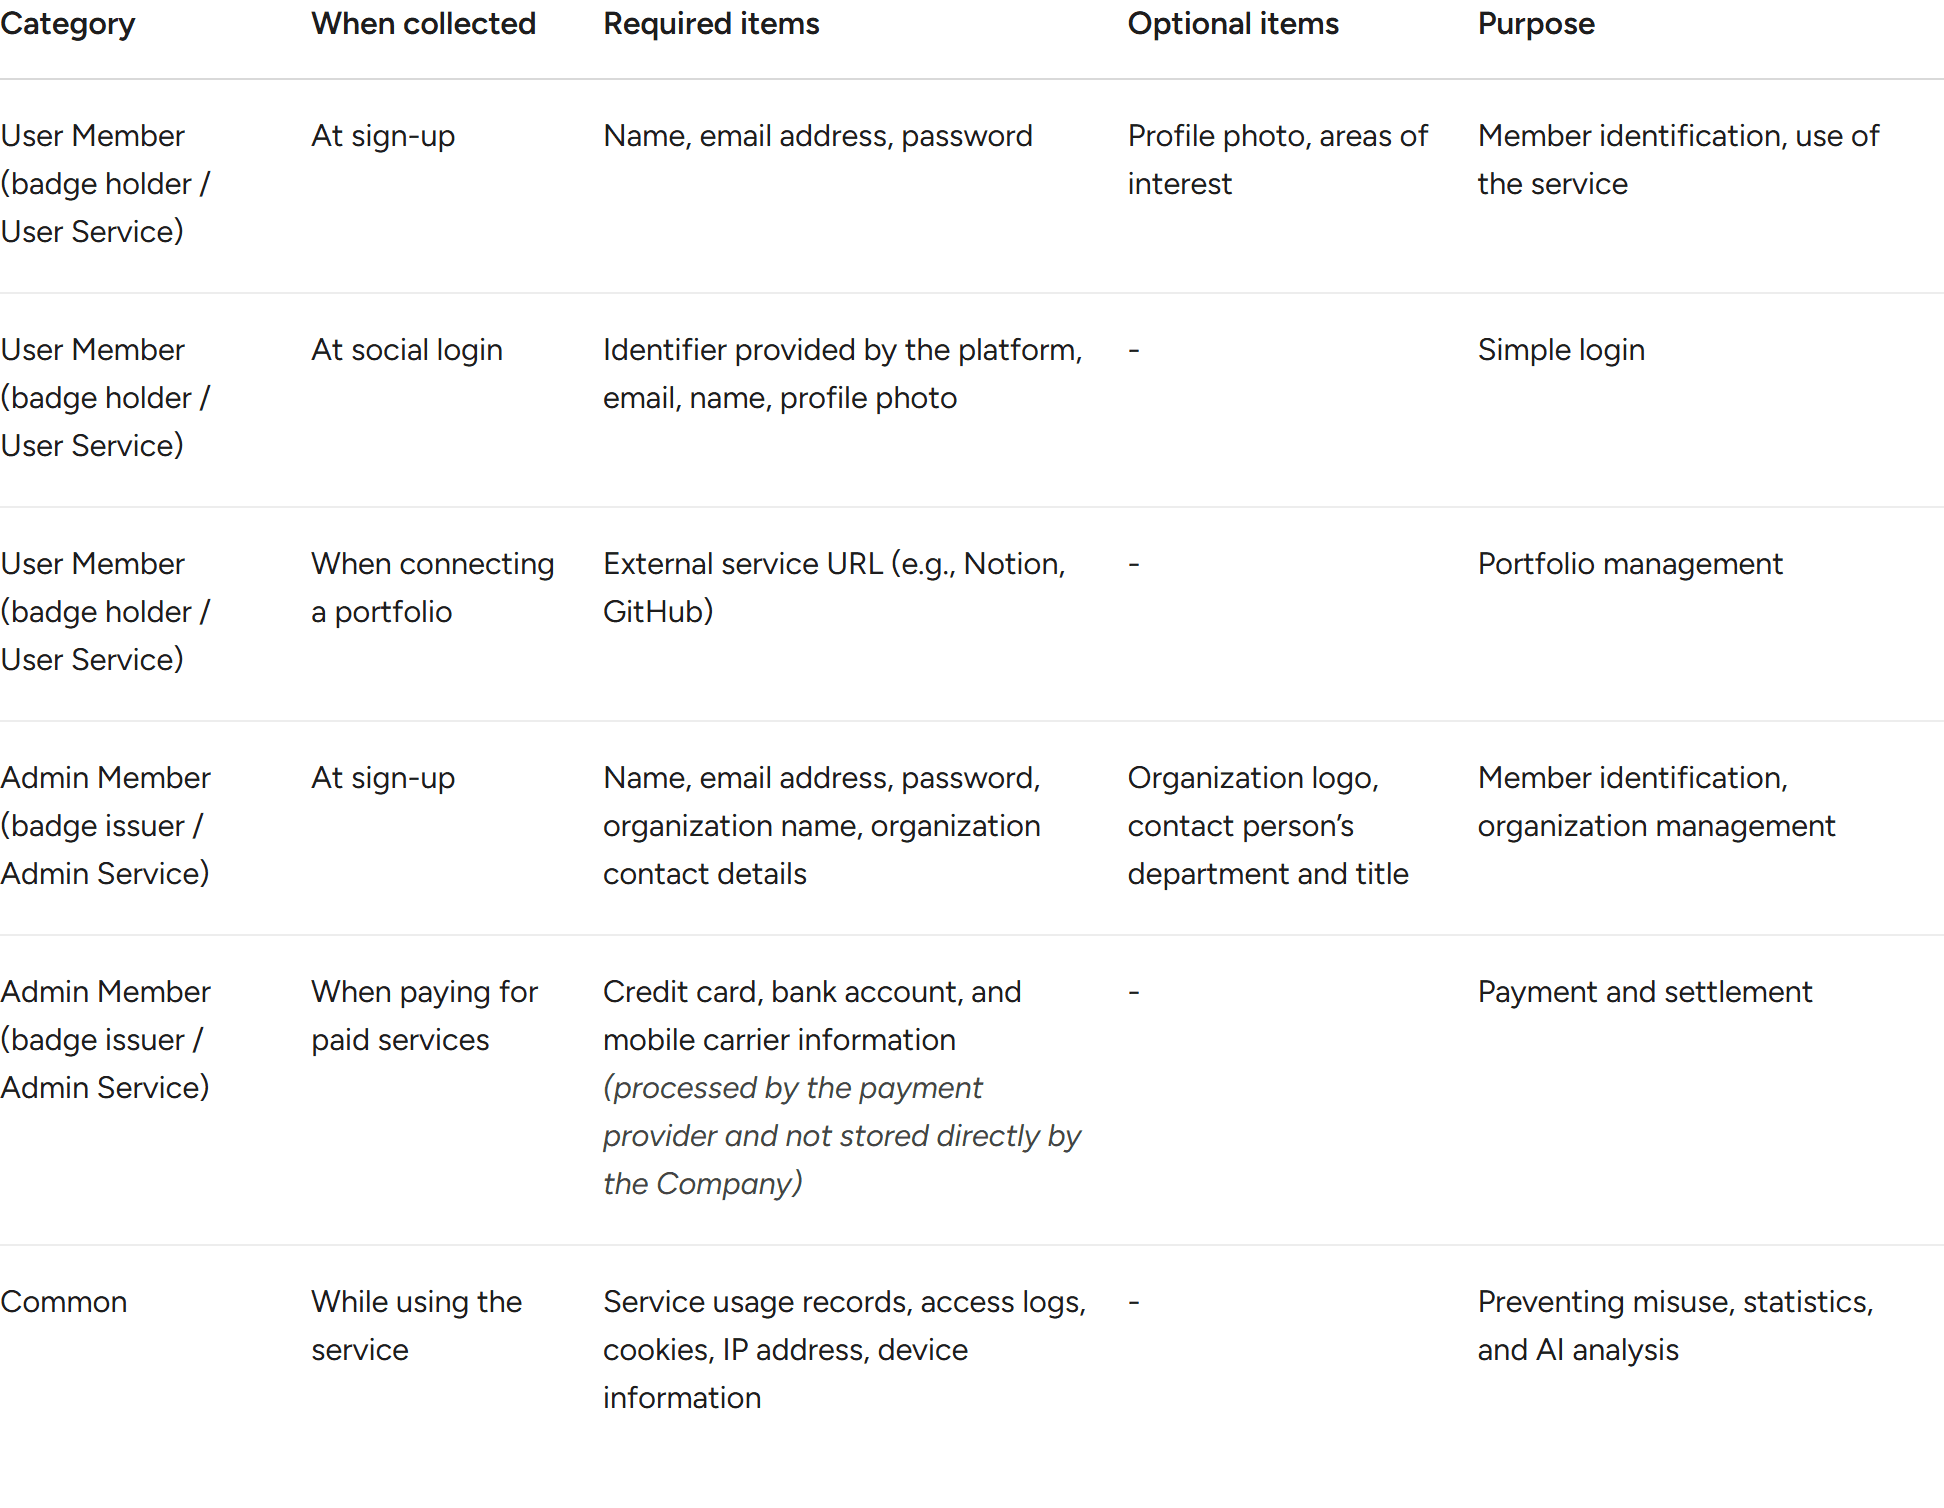
Collection methods
Sign-up through the website (the “User Service” and the “Admin Service”) and changes to information while using the service
Integration through social login
Payment for paid services
Customer support inquiries (email, phone, 1:1 inquiries, etc.)
Automatic collection through log analysis programs while using the service (cookies, access logs, etc.)
[Important] Personal information of ‘badge recipients’ (name, email, phone number, etc.) that Admin Members enter to issue badges is not information the Company ‘collects’ under this Article 3; it is information ‘processed on behalf of’ Admin Members under Article 7.
Article 4 (Processing and Retention Periods)
The Company processes and retains personal information within the retention and use period required by law or agreed to by the data subject at the time of collection.
The processing and retention periods for each type of personal information are as follows:
Member sign-up and management: until membership is withdrawn. However, in the following cases, information is retained until the relevant reason ends.
If an investigation or inquiry for a violation of applicable laws is in progress: until the investigation or inquiry ends
If claims or debts remain from use of the service: until those claims and debts are settled
Preventing misuse: for one year after withdrawal
Service-related records: until the service ends
Information related to issuing, storing, viewing, sharing, and verifying digital badges: retained and used until the badge holder or an issuer with legitimate authority requests deletion, privacy, or suspension of verification, a reason for destruction arises under applicable laws, or the Company ends the Certi service.
However, the expiration of an Admin Member’s paid service period, cancellation of a subscription, non-renewal, or non-renewal of a contract is not considered a reason to end the processing and retention of personal information for storing, viewing, and verifying previously issued digital badges.
Where retention is required by applicable laws such as the Information and Communications Network Act and the Electronic Commerce Act, the Company retains member information for the periods set by those laws, as follows:
Records of contracts or withdrawal of subscriptions (Act on Consumer Protection in Electronic Commerce): 5 years
Records of payment and supply of goods (Act on Consumer Protection in Electronic Commerce): 5 years
Records of consumer complaints or dispute handling (Act on Consumer Protection in Electronic Commerce): 3 years
Login records (Protection of Communications Secrets Act): 3 months
Article 5 (Provision to Third Parties)
In principle, the Company processes users’ personal information within the scope specified in Article 2 (Purposes of Processing Personal Information) and does not process it beyond that scope or provide it to third parties without the user’s prior consent, except in the following cases:
When separate consent has been obtained from the data subject
When required by law, or when requested by an investigative agency following the procedures and methods prescribed by law for investigative purposes
Article 6 (Entrustment of Processing)
To process personal information smoothly, the Company entrusts personal information processing to outside parties as follows.
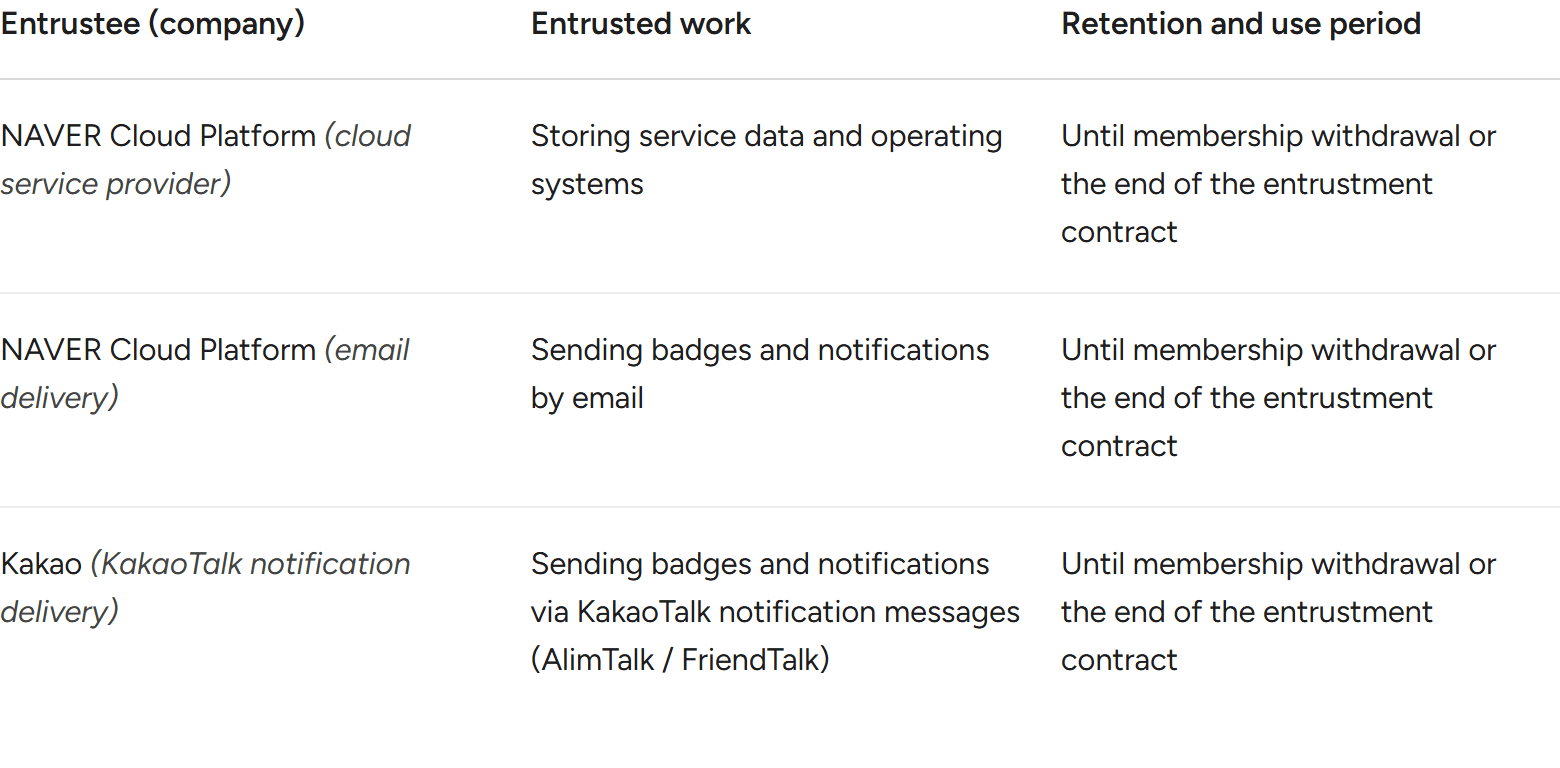
When entering into an entrustment agreement, the Company specifies in a contract or other document, in accordance with Article 26 of the Personal Information Protection Act, the prohibition of processing personal information for purposes other than the entrusted work, technical and administrative safeguards, restrictions on re-entrustment, management and supervision of the entrustee, liability for damages, and other matters, and supervises whether the entrustee processes personal information safely. If the content of the entrusted work or the entrustee changes, the Company will disclose it through this Privacy Policy without delay.
Article 7 (Processing of Personal Information by Admin Members and the Company’s Role)
The Certi service provides a system (entrusted work) that enables Admin Members to issue digital badges to their program graduates and others (“badge recipients”).
In this process, the “personal information controller” for badge recipients’ personal information (name, email address, phone number, etc.) is the “Admin Member” who collected that information and requested badge issuance.
The “Company” acts as a “processor” that processes that personal information at the request of the “Admin Member” (badge issuance).
When collecting the personal information of badge recipients and providing (entrusting) it to the Company, “Admin Members” are responsible for obtaining lawful consent for collection and processing in accordance with applicable laws such as the Personal Information Protection Act.
The “Company” processes personal information entrusted by Admin Members only within the scope necessary to provide the digital badge service, including issuing, sending, confirming receipt of, storing, viewing, and sharing digital badges, generating PDF certificates, confirming issuance and verifying authenticity through verification pages, share links, and QR codes, correcting errors, and customer support, and manages it securely in accordance with applicable laws.
Even if an Admin Member’s paid service period expires, or the subscription is canceled or not renewed, or the contract is not renewed, the Company may continue to process the minimum personal information necessary to confirm issuance and verify the authenticity of previously issued digital badges during the retention period set out in Article 4. In this case, personal information is processed only to the extent needed to provide verification of previously issued digital badges, separately from whether new badges are issued, admin features are provided, or technical support and maintenance are provided.
Article 8 (Rights and Obligations of Data Subjects and Legal Representatives, and How to Exercise Them)
Data subjects (User Members and Admin Members) may exercise the following rights regarding personal information protection against the Company at any time:
Request to access personal information
Request to correct errors
Request for deletion
Request to suspend processing
Rights under Paragraph 1 may be exercised in writing, by phone, by email, by fax, or by other means, and the Company will act on them without delay.
If a data subject requests correction or deletion of errors in personal information, the Company will not use or provide that personal information until the correction or deletion is completed.
Rights under Paragraph 1 may be exercised through a representative, such as the data subject’s legal representative or a person delegated by the data subject. In this case, a power of attorney in the form of Annex 11 of the Enforcement Rules of the Personal Information Protection Act must be submitted.
Data subjects must not infringe the personal information or privacy of themselves or others processed by the Company in violation of applicable laws such as the Personal Information Protection Act.
Data subjects may control and use their own information by viewing their digital badge information or connecting (sharing) it to external platforms (e.g., LinkedIn) through functions provided on pages such as ‘My Badges,’ thereby exercising rights equivalent to the ‘right to request transmission of personal information’ under the Personal Information Protection Act.
Requests to access, correct, or delete the personal information of ‘badge recipients’ entrusted by Admin Members under Article 7 should, in principle, be directed to the Admin Member who is the ‘personal information controller’ of that information.
User Members or badge recipients may view, share, download, and check verification links for digital badges they have received, and may request access to, correction or deletion of, or suspension of processing of their personal information, or that a verification page be made private, in accordance with applicable laws. However, where there are legitimate reasons such as proving the fact of issuance, responding to disputes, or fulfilling legal obligations, the Company may retain necessary information to the extent permitted by applicable laws.
Article 9 (Procedures and Methods for Destroying Personal Information)
When personal information is no longer needed, such as when the retention period has passed or the purpose of processing has been achieved, the Company destroys it without delay.
If personal information must continue to be retained under other laws, as in Article 4(3), even though the retention period agreed to by the data subject has passed or the purpose of processing has been achieved, the Company moves it to a separate database (DB) or stores it in a different location.
Information for confirming issuance and verifying the authenticity of digital badges is destroyed when the retention period set out in Article 4 or the purpose of providing verification ends. However, while storage, viewing, and verification of previously issued digital badges are provided, the purpose is considered to continue.
The procedures and methods for destroying personal information are as follows:
Destruction procedure: the Company selects personal information for which a reason for destruction has arisen and destroys it with the approval of the Company’s Chief Privacy Officer.
Destruction method: personal information recorded and stored as electronic files is destroyed using technical methods that make the records unrecoverable, and personal information recorded and stored on paper is shredded or incinerated.
Article 10 (Measures to Ensure the Security of Personal Information)
To ensure that users’ personal information is not lost, stolen, leaked, altered, or damaged, the Company takes the following technical, administrative, and physical measures:
Administrative measures: establishing and implementing an internal management plan, regular staff training, etc.
Technical measures: managing access rights to personal information processing systems, installing access control systems, encrypting unique identification information, and installing security programs
Physical measures: controlling access to computer rooms, data storage rooms, etc.
Article 11 (Installation, Operation, and Refusal of Automatic Personal Information Collection Devices)
The Company processes and retains personal information within the retention and use period required by law or agreed to by the data subject at the time of collection. In the course of providing the Service, the Company may also collect information generated automatically while the Service is used, such as service access and usage records, IP addresses, browser types, device information, and cookies. The Company uses this information to provide and stably operate the Service, including keeping members logged in, security and fraud prevention, identifying service failures, improving the usage environment, and statistical analysis.
The processing and retention periods for each type of personal information are as follows:
Member sign-up and management: until membership is withdrawn. However, in the following cases, information is retained until the relevant reason ends.
If an investigation or inquiry for a violation of applicable laws is in progress: until the investigation or inquiry ends
If claims or debts remain from use of the service: until those claims and debts are settled
Preventing misuse: for one year after withdrawal
Service-related records: until the service ends
Where retention is required by applicable laws such as the Information and Communications Network Act and the Electronic Commerce Act, the Company retains member information for the periods set by those laws, as follows:
Records of contracts or withdrawal of subscriptions (Act on Consumer Protection in Electronic Commerce): 5 years
Records of payment and supply of goods (Act on Consumer Protection in Electronic Commerce): 5 years
Records of consumer complaints or dispute handling (Act on Consumer Protection in Electronic Commerce): 3 years
Login records (Protection of Communications Secrets Act): 3 months
Article 12 (Chief Privacy Officer and Responsible Department)
The Company designates the following Chief Privacy Officer to take overall responsibility for personal information processing and to handle data subjects’ complaints and remedies related to personal information processing.
Chief Privacy Officer (CPO) : Seokhoon Kang
Department : Development Team
Contact : [info@nftime.world]
Data subjects may contact the Chief Privacy Officer and the responsible department with any inquiries, complaints, or requests for remedies regarding personal information protection arising from use of the Company’s services. The Company will respond to and handle such inquiries without delay.
Article 13 (Remedies for Infringement of Rights)
To obtain remedies for infringement of personal information, data subjects may apply for dispute resolution or consultation to the Personal Information Dispute Mediation Committee, the Korea Internet & Security Agency’s Personal Information Infringement Report Center, and other bodies. For other reports and consultations about personal information infringement, please contact the following organizations:
Personal Information Dispute Mediation Committee: 1833-6972 (no area code, Korea) (www.kopico.go.kr)
Personal Information Infringement Report Center: 118 (no area code, Korea) (privacy.kisa.or.kr)
Supreme Prosecutors’ Office: 1301 (no area code, Korea) (www.spo.go.kr)
Korean National Police Agency: 182 (no area code, Korea) (ecrm.cyber.go.kr)
Article 14 (Changes to the Privacy Policy)
The content of this Privacy Policy may change due to government policy or the Company’s needs. If there are any additions, deletions, or modifications, the Company will announce them through ‘Notices’ in the Service at least 7 days before the revision.
Announcement date: April 28, 2025
Effective date: April 28, 2025